Glossary
A-C | D-F | G-K | L-O | P-T | U-V | W-Z
Ad blocker – technology that disables banners, pop-up windows, trackers, and embedded audio and video files on webpages and mobile applications. The easiest way to restrict disruptive ads is to install browser extensions and applications. This type of software operates by filtering ad elements using blocklists. These lists are downloaded and used by the extension, enabling it to block or hide ads when they appear. For users, ad blockers provide numerous benefits, including faster website loading, cleaner-looking webpages, lower resource usage (such as memory), and increased digital security.
Address Resolution Protocol (ARP) – network protocol used for mapping MAC addresses to known IP addresses on a local network. ARP was developed to transmit IP packets across Ethernet networks.
Administrator – this term has multiple meanings in computing. Usually, it is a person responsible for the operating environment in an information system. Duties vary and differ from one organization to another. System administrators install, support, and manage servers and other computer systems. In addition, they may handle system security, user permissions, and technical project management.
Adversary – a malicious entity aimed at violating users’ confidentiality, data integrity, and system availability. Their activity extends to discovering private data, corrupting system information, spoofing identities, and forcing system outages. Adversaries are commonly classified:
- In terms of computational limits (computationally bounded and unbounded attackers)
- According to behavior and visibility, including passive (eavesdropping) and active (Byzantine)
- Based on strategy (static and adaptive)
- In the context of mobile or networked systems (localized and mobile adversaries)
AES (Advanced Encryption Standard) – a symmetric-key algorithm established as a standard by the US government (NIST). Based on the Rijndael cipher, AES encrypts data in 128-bit blocks using a secret key of 128, 192, or 256 bits. To decrypt received blocks, it performs the reverse process using the same secret key. AES is thoroughly analyzed and widely considered a secure tool for protecting sensitive and classified information.
Anonymity – the state of keeping an individual's identity, origin, and actions hidden. Technically, anonymity is pursued using various tools and protocols: proxy servers, VPNs, SSH tunnels, Tor, and I2P provide varying degrees of privacy, though each involves tradeoffs (such as reduced speed or complex configuration). Absolute anonymity cannot be guaranteed, as security depends on resisting traffic analysis, operational security errors, and resource-heavy surveillance.
API – stands for Application Programming Interface. It is a set of defined functions, procedures, and data formats offered by an application, operating system, or library that external software can use to interact with it. APIs allow developers to integrate services and build applications without rebuilding underlying functionality.
AppleTalk – a proprietary suite of protocols developed by Apple for networking Macintosh computers. Introduced in 1984, networking capabilities were built directly into Mac hardware and software, making AppleTalk simple to set up compared to alternatives at the time. It was eventually phased out in favor of TCP/IP. The suite included protocols for reliable byte-stream transmission (ADSP), session control (ASP), routing across networks (AURP), printer communications (PAP), and network zone mapping (ZIP).
ARP spoofing – an attack technique on local Ethernet networks where an attacker sends forged ARP messages, linking their MAC address to the IP address of a legitimate host to intercept or modify traffic.
Authentication – a verification procedure. It may be a credential check when an entered password is compared with the record from a user database, or email authentication by digital message signature verification. Depending on credibility value and a system's security policy, authentication is often backed by cryptographic methods.
Authorization – an empowering of a certain person or a group of individuals to take specific actions. It is also a verification process when attempting to allow actions. The term is close to authentication, but it is responsible for access control to system resources following successful authentication. Generally, these two procedures may overlap. Authorization is widely distributed in banking (payment and credit cards usage) and business (license granting) sectors.
Backdoor – an algorithm or system defect that is deliberately built by a designer and allows gaining secret access to databases and remote control. A backdoor may be embedded in an encryption algorithm or system to enable bugging of a secure channel. An ideal backdoor is difficult to detect. If a backdoor is disclosed, it is often difficult to determine who the exploiter was and what information was compromised.
Biometric authentication – a verification method that operates with an individual's biometric data to identify them. The system records biometric traits with a capturing device (e.g. takes a user face picture). Further, it elicits distinct traits from the biometric specimen using a feature extractor program algorithm. The system stores these features as a database template together with user identity details. To pass the authentication process, a user presents the requested feature. The program compares it with the template and decides on granting access.
Bitcoin – a modern distributed digital currency created and operated on the Internet. This is an independent payment system, the emission of which is achieved through computer performance all over the world using mathematically based algorithms. The system was created by Satoshi Nakamoto, whose identity remains unrevealed to this day, and exists in the form of transaction records accomplished between addresses. Its fundamental distinctions include:
- decentralization;
- ease of use;
- pseudonymity;
- transparency;
- nominal commission;
- transaction processing;
- irrevocable money transmission.
Bitcoin mixing – a special service which splits the bond between old and new addresses when sending finances from one customer to another. The program mixes received BTC and distributes them into new wallets, breaking the direct link between transactions. The process can be repeated to obscure the flow of funds. Depending on the required anonymization layer and mixable resources number, the process takes more time to match a necessary number of mixing partners. Seeing that anonymizing BTC often proceeds on remote servers of a centralized mixer, monitoring and process logging are possible, which doesn’t guarantee 100% anonymity.
Bitcoin wallet – it keeps the secret private key required for accessing a bitcoin address and can be represented by anything from a piece of paper to modified software on a USB flash drive. In a technical sense, a wallet stores secret digital keys connected with a public bitcoin address, providing the ability to control transactions. There are various types of storage, but all of them can be divided into four general classes:
- for personal computers;
- for mobile devices;
- online wallets;
- hardware-based wallets.
BitTorrent – a P2P network protocol for cooperative data exchange over the Internet. Files are distributed portion-wise. Every torrent client receives/downloads these parts and meanwhile distributes/uploads them to others. This process decreases traffic strain and dependence on a single client-source, and guarantees data redundancy.
Block chain – a series of blocks which contain records of executed transactions and a header. Newly created blocks are appended to the series and are tamper-resistant. Headers involve their own hash, info concerning the previous chain’s block, a Merkle root hash, and additional operational info. In such a manner, a blockchain forms an immutable ledger that can be verified from dedicated websites or network nodes.
Browser extension – a computer program that expands browser functional capabilities. Depending on the browser, the term may differ. An extension most commonly improves security, accessibility, blocks advertisements, and improves the browser interface. It adds multiple features to make surfing the Internet easier and more enjoyable. A plug-in is an external computing unit that connects to a host program to expand capabilities, usually implemented via shared access libraries. An add-on extends browser functionalities like other listed pieces of programs, notably associated with the Mozilla ecosystem.
Browser fingerprint – a technique driven by gathering info that is sent to a visited website. It involves language preferences, installed fonts, clock zone, screen resolution, installed plugins, etc. By doing so, it creates a well-rounded image of the browser, resembling a fingerprint. Even if all cookies have been deleted, a resource can recognize a particular user. Changing an IP address alone is often not enough. Browser fingerprints make devices recognizable across digital resources, posing a notable privacy concern.
Canvas fingerprinting – a covert identification method recognizing visitors when accessing a website. This technology is resistant to standard blocking measures, such as cookie deactivation or basic ad blockers. While visiting a resource with an installed tracking script, the browser is instructed to draw a hidden image or text using the HTML5 canvas. The image renders with subtle variations depending on browser version, OS, and GPU. The resulting image is hashed and used as a unique fingerprint assigned to the device.
Certificate Authority (CA) – a trusted organization responsible for issuing digital certificates. The CA's principal function is to verify public keys by utilizing digital signatures. It acts as an essential component of public key infrastructure (PKI) and is responsible for managing public key certificates. Public keys and identity materials are kept in these certificates.
Closed source software – software which allows binary (compiled) product distribution only and maintains inaccessibility of the initial programming code, restricting third-party modifications. Access to source code is only provided to third parties under specific arrangements, such as signing a nondisclosure agreement. An operating system with closed code is a proprietary computer program distinct from free and open-source software definitions.
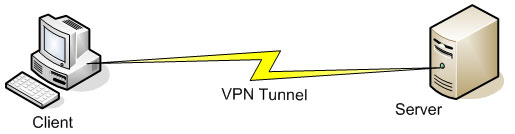
Client/Server VPN – it secures data transferring between a client node and a server in a network. As a particularity, a VPN creates a virtual encrypted bridge binding two endpoints (e.g. between a workstation and a server). It is often provided to establish logical segmentation within one physical network. This is a way to isolate traffic between different departments using the same physical network segment, functioning similarly to a VLAN with added traffic encryption.
Computer virus – a widespread sort of malicious software that harmful affects computer programs. It is intended to gain unsanctioned access to computing resources or stored information. A virus infects a computer and compromises confidential material by copying, corrupting, or deleting files. Malware can also spam email contacts, display undesirable notices on a user’s screen, and make machines inoperable.
Connection Log – a record of network events (e.g. user connections and actions over the network) maintained by a program or information system. It is an automatic process recorded without human input. The logging includes recording in a special file or database, marking with a timestamp and source identifier, gathering identical or analogous records, and managing old records.
Cookies – text files that are stored by applications (usually browsers) for different purposes. These small pieces of data hold session values and serve to authenticate the user. The software keeps personal preferences and settings, monitors session state, and gathers user statistics. In addition to privacy concerns, working with cookies may cause security vulnerabilities if unencrypted, such as susceptibility to session hijacking.
Copyright trolls – an individual or an organized group that enforces copyrights primarily in order to acquire money through aggressive legal and court threats. They pursue alleged piracy, file mass complaints, and demand statutory compensation. Such activity is often criticized, as it is viewed as exploiting legal pressure rather than protecting creative works.
Cryptocurrency – a type of digital currency where accounting and emission are established by cryptographic methods. Its functioning proceeds in a decentralized, distributed computer network. The first and most popular payment system is Bitcoin. With cryptocurrency, clients conduct peer-to-peer transactions without a middleman, transferring value directly to a recipient. Coins are validated on a blockchain ledger, and digital assets can be bought, received as payment for services, or traded between individuals.
Cyber threat – an illegal infiltration or a threat of malicious access to digital environments, targeted at achieving political, financial, or disruptive goals. It affects computer systems containing information and files on physical and virtual devices. An attack may compromise a storage medium that stores, filters, or transmits personal information. Cyber threats come from hackers, malicious groups, and advanced actors capable of bypassing server protection mechanisms to extract data.
Dark Web – a World Wide Web segment composed of overlay networks and darknets that use the public Internet but require special software, configurations, and authorization to gain access. It forms part of the deep web and is represented by websites where users’ identities and server locations are hidden. Standard search engines and default web browser settings do not access Dark Web pages. The Dark Web can be a shelter for free speech and privacy in censored regimes, but on the other hand, it hosts black markets that trade in contraband, illegal goods, and cybercrime services.
Data confidentiality – measures taken to safeguard sensitive information and prevent unauthorized access to it. Data encryption and multi-factor authentication are standard protective methods. Other prevention practices involve secure browser usage (such as Tor), hardware security tokens, and biometric verification. If information is extremely sensitive, extra measures may be taken, including physical air-gapping and offline storage.
Data authentication – a process to verify that transmitted data was genuinely sent by the asserted conversant. In two-sided communication, verification can be accomplished through straightforward mechanisms: parties share a key or utilize digital signatures to verify a message authentication code (MAC) on transported data. When the MAC or signature validates correctly, participants can be confident of the source and integrity of the transmission.
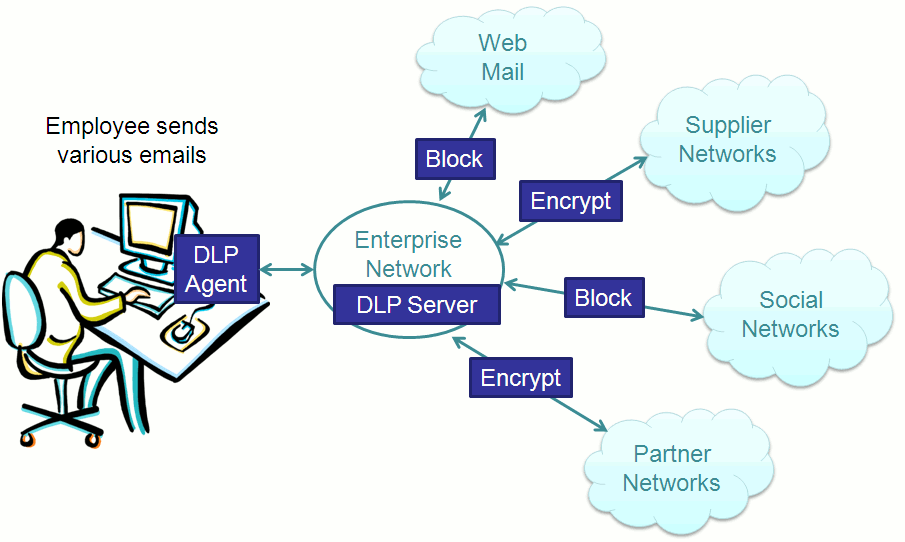
Data Leak Prevention (DLP) – technologies that prevent confidential information from leaking outside an information system. DLP systems are built on analyzing data flows that cross a protected network perimeter or exist on endpoints. If confidential information is detected in unauthorized transfers, the DLP system activates and blocks the transfer.
Datagram – an independent information unit transferred by a network protocol without preset connection establishment or virtual circuit maintenance. A datagram protocol provides connectionless network service and does not inherently guarantee delivery order, error-free arrival, or packet deduplication. Examples include IP and UDP.
Datagram Transport Layer Security (DTLS) – ensures communication security for protocols leveraging datagrams. The protocol supports protected communication between datagram-based applications. It prevents information interception, tampering, and message forgery while preserving data integrity. DTLS is based on the stream-oriented TLS protocol and provides equivalent security for connectionless traffic.
Data protection – legal and technical measures focused on safeguarding personal and sensitive data. Appropriate safeguards are taken against unauthorized access, prohibited data abuse, and accidental loss or damage. Personal data must be protected against unlawful public disclosure, under conditions set in the legal systems of states and international organizations (such as the GDPR).
DD-WRT – a free, open-source firmware replacement for wireless consumer routers based on Broadcom, Atheros, and other chipsets, permitting users to configure local network parameters in a flexible manner. DD-WRT supports advanced functions often excluded from original firmware, such as daemon-based services, Wireless Distribution System (WDS), QoS bandwidth controls, custom startup scripts, and IPv6 support.
Deanonymization – an infringement of anonymity that involves revealing a web user's real personal identity (such as real name, residence, or job title). The process can occur on public forums, blogs, or wikis. A voluntary deanonymization happens when a participant consciously or accidentally shares identifying details. Involuntary deanonymization occurs when an observer correlates metadata, IP addresses, or tracking details to expose the individual without their consent.
Decryption (deciphering) – a cryptographic process reverse to enciphering. This process decodes ciphertext back into readable plaintext using an appropriate decryption key. Special deciphering software or algorithms are used to restore the original data.
DES (Data Encryption Standard) – a symmetric encryption algorithm by IBM and approved by the US government in 1977 as an official standard (FIPS 46). A Feistel cipher underlies the algorithm, which has a 56-bit key length.
Direct Access (Unified Remote Access) – a remote access feature in enterprise Windows environments. Client devices connect to DirectAccess servers automatically as soon as they connect to the Internet. While classic VPNs are typically activated manually by user actions, DirectAccess tunnels are created transparently. It relies on IPv6 connectivity, utilizing transition technologies like 6to4, Teredo, or IP-HTTPS to transmit traffic across IPv4 networks.
DMCA notice (Digital Millennium Copyright Act) – a formal request sent to online service providers and web hosts asking them to remove content alleged to violate copyright. This notice provides a legal framework under US law, offering hosts safe-harbor protection if they act expeditiously to take down infringing content upon proper notification.
DMVPN (Dynamic Multipoint VPN) – a Cisco technology that provides the possibility to build dynamic secure channels between multiple sites. A branch site connects to a central DMVPN hub to receive routing information, after which it can create dynamic, direct virtual IPsec tunnels to other spoke routers on demand. In such a manner, the system scales efficiently and offloads central servers.
DNS (Domain Name System) – a system that translates internet hostnames into networking addresses. DNS servers convert human-friendly domain names into numerical IP addresses, making requested network resources accessible to computers.
DNS leak – a security vulnerability where DNS requests are sent outside an encrypted VPN or proxy tunnel directly to an ISP's DNS servers. If DNS requests bypass the secure tunnel, it discloses the user's browsing activity and approximate geographic location. DNS leaks can also occur through browser technologies such as WebRTC.
DOM storage (Document Object Model) – a component of HTML5 Web Storage designed as an extended and more secure alternative to storing data in HTTP cookies. With this mechanism, key/value pairs are stored locally on the client and are not sent automatically to the server with every HTTP request. Its main aim is to provide web applications with structured client-side storage.
DRD (EU Data Retention Directive) – an EU regulatory directive adopted in 2006 that required telecommunications and internet providers operating in Europe to store customer telephone, IP, and connection metadata for a period between 6 months and 2 years. In 2014, the Court of Justice of the European Union declared the directive invalid because it violated fundamental privacy rights.
Dynamic VPN IP – a VPN configuration where a user is assigned a shared, changing IP address from a chosen location rather than a fixed address. Dynamic address management masks the user's personal IP across the Internet. The client’s real identity stays obscured behind the VPN server's shared address.
Encryption – a process converting plaintext into a cipher using a specific cryptographic key. This procedure is applied to prevent unauthorized parties from accessing and reading protected materials. There are two primary forms: symmetric algorithms, which use the same private key for both locking and unlocking, and asymmetric algorithms, which utilize a public key for encryption and a distinct private key for decryption.
Encryption key length – the number of bits in a cryptographic key utilized by an algorithm, representing the strength of the cipher. Keys control the transformation of data such that only the correct key can restore encrypted files to plain text. Keys must be sufficiently long to withstand brute-force attacks and guarantee secure data exchange.
End-to-end (e2e) encryption – a communication architecture where the keys needed to encrypt and decrypt messages are held solely by the communicating endpoints. Messages and attachments that pass through intermediate servers remain in an unreadable form, and only the intended recipient is able to decrypt and read the contents. Tools like PGP and secure messaging apps utilize E2E encryption to guarantee message privacy.
End-to-end timing attack – a side-channel attack where an adversary attempts to compromise a cryptosystem by measuring the time required to execute cryptographic operations. Because different inputs or computations can take varying amounts of time, an attacker with high-precision time measurements may analyze these variations to reconstruct secret keys or data.
ETag (entity tag) – an HTTP identifier assigned by web servers to specify a particular version of a resource located at a URL. If the content at this address changes, a new ETag is assigned. In such a manner, an ETag is analogous to a fingerprint, allowing clients and servers to compare tags and determine whether cached files are identical, which improves caching efficiency and saves bandwidth.
Extranet VPN – a VPN deployment that connects external partners, customers, or suppliers to designated portions of a company's internal network. Because these outside parties are not fully inside the corporate boundary, strict access controls and firewalls are implemented to limit their access to sensitive internal systems.
Geo-blocking – a restriction technique that limits access to internet content depending on a user's geographical position. Websites and streaming platforms determine a visitor's location by inspecting their public IP address. Geo-blocking is widely used to enforce international licensing, copyright contracts, or regional regulatory compliance.
File sharing – the process of distributing and transmitting digital media, including software applications, documents, and multimedia files. It can be managed with access controls, granting read-only or read-and-write permissions to specific groups. Popular methods include peer-to-peer (P2P) file sharing, which enables decentralized file exchange directly between users.
Firewall – a security system that monitors and filters network traffic to protect devices against unauthorized access. The capabilities of a firewall include network traffic inspection, controlling which applications access the Internet, blocking port intrusions, and filtering unwanted connections based on security rules.
Firefox – a free, open-source web browser developed by the Mozilla Foundation. Among its primary features are customizable architecture, tracking protection tools, and high-performance browsing. Firefox supports thousands of add-ons for downloading media, password management, and privacy enhancements.
Five Eyes – an intelligence alliance comprising the United States, the United Kingdom, Canada, Australia, and New Zealand, based on historical signals intelligence agreements. Declassified files have shown that member countries cooperate extensively on joint intelligence gathering and surveillance data sharing.
Flash cookies (or Local Shared Objects/LSO) – data files stored on a user’s computer by the Adobe Flash Player runtime. Similar to standard cookies, LSOs were used by websites and advertisers to store user preferences and tracking data. Because Flash cookies were stored independently of browser cookie caches, they did not clear when standard cookies were deleted, functioning as persistent tracking tokens until the deprecation of Flash.
Gag order – an official legal order restricting individuals or organizations from disclosing information regarding legal proceedings, subpoenas, or national security requests to third parties. In computing and telecommunications, gag orders are often served alongside government data requests to prevent service providers from alerting targets.
GCHQ (Government Communications Headquarters) – the UK intelligence agency responsible for signals intelligence (SIGINT) and providing cybersecurity guidance for the British government and armed forces. GCHQ conducts electronic communications interception and surveillance operations in cooperation with international partners such as the US NSA.
Geo-spoofing – a method of masking or changing an apparent geographical position by using a proxy or VPN server in another location. This allows users to browse resources with a different regional IP address, protecting local privacy or bypassing regional geo-restrictions.
Hamachi – a hosted software application that connects computers over the Internet to create a secure, virtual private network using standard encryption algorithms. An encrypted connection is formed between devices across NAT routers without complex network configuration, allowing users to establish private networks for gaming, file sharing, and remote access.
Handshake – an automated negotiation process between two network nodes used to establish a secure communications channel. During the handshake, endpoints authenticate identities, agree on compatible protocol versions, and negotiate cipher suites and encryption keys for subsequent data transmission.
Hashing – a method of transforming incoming data of arbitrary length into a fixed-length string of characters using a mathematical algorithm. In computer security, cryptographic hashing functions are essential tools used for storing passwords safely, verifying file integrity, and creating digital signatures.
History stealing – a web privacy vulnerability allowing a malicious website to discover which URLs a visitor has previously visited. Historically, this was achieved by injecting hidden links and checking their visited styling via JavaScript. Modern browsers have patched this behavior to prevent unauthorized access to browser history.
HTTPS (HyperText Transfer Protocol Secure) – an extension of the HTTP protocol that incorporates SSL/TLS encryption . It is HTTP transmitted through an encrypted transport layer. HTTPS protects network communications against eavesdropping and tampering by authenticating servers via digital certificates and encrypting all traffic.
I2P (Invisible Internet Project) – an anonymous, decentralized overlay network designed to protect data exchanges from surveillance. I2P is built for end-to-end encrypted messaging, hosting internal hidden services, and secure peer-to-peer file sharing, using layered garlic encryption to resist traffic analysis.
ICS (Internet Connection Sharing) – a feature built into Microsoft Windows (introduced with Windows 98 Second Edition) that allows a computer connected to the Internet to act as a gateway, sharing its connection with other computers on a local area network using NAT and DHCP.
Identification – the process of establishing or asserting an identity within a system (such as entering a username or account handle). In web tracking, identification can also refer to profiling users by analyzing static IP addresses, cookies, and distinctive browser characteristics.
Identifier – a unique feature of a subject that distinguishes it from other devices or entities. The identification procedure assigns a corresponding ID number and uses it to identify the subject. It may be a sequence of special symbols (e.g. an underscore), digits, and upper- and lowercase Latin letters.
IKEv2 (Internet Key Exchange) – a standard IPsec protocol designed to establish and manage Security Associations (SAs) and exchange keys. It includes mechanisms to protect against certain denial-of-service attacks.
Information security – a set of measures focused on maintaining the confidentiality, availability, and integrity of information. It protects information systems against data leaks and unauthorized or inadvertent changes to system resources. Management principles are usually introduced in an organizational security policy, a set of rules, procedures, and best practices for cybersecurity.
Internet censorship – the monitoring or suppression of information published on or accessed through the Internet. Even if a country’s legislation prohibits certain content on domestic resources, it may remain available on web servers in other countries. Governments or political regimes may control network communications by blocking or closing web resources, analyzing traffic, or penalizing authors, site owners, and other parties.
Internet traffic – the flow of data across the Internet over a given period. The amount of traffic is measured in bits or bytes and their multiples (KB, MB, GB, etc.). It can be categorized as outgoing (when information passes to an external network), incoming (when information arrives from an external network), internal (data flows within a network), or external (data passes beyond a specified network).
Internet VPN – a type of private network used by service providers to grant access to the Internet. It may be used when multiple users connect through a shared physical channel.
Intranet VPN – an internal private network that links corporate headquarters or offices. It provides an organization with a private network for sharing materials, such as employee lists and telephone numbers of partners and clients.
IP (Internet Protocol) – a network-layer protocol that connects separate computer networks. It is responsible for delivering data between network nodes. Like an address on a letter, an IP address helps identify where a packet should go. However, IP cannot guarantee reliable delivery: packets may arrive out of order, be duplicated, or be damaged in transit.
IP leak – an anonymity threat in which a user’s real IP address is exposed despite an active VPN connection. WebRTC, IPv6 routing, or VPN connection failures can contribute to IP leaks. To reduce the risk, users can configure their browser and VPN appropriately.
IP guard – a facility intended for monitoring user activity, controlling network access, and protecting sensitive and corporate data. It should not be confused with IP Source Guard, a switch feature that helps prevent IP address spoofing.
IP spoofing – a type of network attack in which an attacker uses a forged source IP address, for example, to conceal the sender’s identity or bypass some security controls.
IPv4 (Internet Protocol version 4) – uses 32-bit addresses, providing approximately 4.3 billion possible addresses. The traditional format consists of four decimal numbers from 0 to 255, separated by periods. The exhaustion of unallocated IPv4 addresses became a significant issue as Internet use grew; the remaining address pools were exhausted at the regional registry level over time.
IPv6 (Internet Protocol version 6) – a newer version of IP intended to address IPv4 address exhaustion by using 128-bit addresses. IPv4 and IPv6 can operate together using dual-stack configurations. Adoption of IPv6 varies among providers and networks, and older devices may require updates or replacement to support it.
IPX (Internetwork Packet Exchange) – a network-layer protocol in the IPX/SPX suite. It was designed for datagram transfer and does not require a connection to be established first. Servers running Novell NetWare and end stations used the protocol. An IPX address includes a network number, usually assigned by an administrator, and a node number, often based on the MAC address. IPX has largely been superseded by TCP/IP.
ISP (Internet Service Provider) – an organization that provides Internet access (including broadband, dial-up, and wireless connections) and may offer related services, such as web hosting, email, virtual servers, and colocation.
Kerckhoffs’s principle – a cryptographic principle stating that a cryptosystem should remain secure even if everything about it, except the secret key, is publicly known. The security of the system should depend on the secrecy of the key, not on keeping the algorithm or protocol secret.
Key schedule – an element of a block cipher that derives a sequence of subkeys from the encryption key. These subkeys are used during the cipher’s rounds. A well-designed key schedule helps support the cipher’s security.
Kill switch – a technology included in some VPN services that blocks Internet traffic if the encrypted tunnel unexpectedly disconnects. This informs the user of the interruption and helps prevent data from being sent outside the VPN tunnel.
L2f (Layer 2 Forwarding Protocol) – a technique that constructs VPN tunnels over the Internet. L2F does not itself encrypt or protect the information flow; it is an encapsulation protocol. Like PPTP, it was developed for tunneling remote-access traffic to enterprise networks. L2F is independent of IP and uses PPP for remote-user authentication.
L2TP (Layer 2 Tunneling Protocol) – a VPN protocol responsible for tunneling. L2TP does not provide encryption on its own, so it is often paired with IPsec to protect traffic. The protocol is supported by many modern operating systems and devices. L2TP/IPsec may require additional router configuration and can be slower than some alternatives.
Logs – files containing chronological records of events, including system activity and external events. Server log files may record user or program activity on a server. For example, a web server may log visitors’ IP addresses, access times, requested pages, and browser information. Analyzing logs can help administrators understand system use and troubleshoot problems.
Metadata – information that describes other information or an object, including its characteristics and context. Metadata can help people and systems search for and manage data. For example, it may describe a file’s name and size or information about its content.
Mobile VPN – a VPN designed to support mobile devices that frequently change networks and IP addresses. These changes can interrupt traditional VPN connections. Mobile VPNs use mechanisms to help maintain a connection when a device switches networks. Some VPN protocols, including IPsec and TLS-based protocols, can support mobile use.
Multi Logins – a function that allows users to sign in to multiple accounts on the same website using one browser profile. This makes it quick and convenient to switch between accounts. Some multi-login applications also include privacy or security features.
Multi-factor authentication (MFA) – a multistep process for controlling access to a computer system. A user must successfully provide two or more authentication factors to gain access. Factors may include something the user knows (such as a password or PIN), has (such as a security key), or is (such as a biometric trait). Two-factor authentication (2FA) is a type of MFA. A common example is entering a password and then a verification code.
Multi-protocol label switching (MPLS) – a scalable, protocol-independent mechanism for transferring data. In an MPLS network, packets are labeled, and forwarding decisions are based on those labels rather than on examining the packet’s full network-layer header at every hop. MPLS can be used to create virtual paths across a network.
N2n – a VPN technology implementation with open-source code. It builds encrypted point-to-point tunnels between computers. The program can connect devices behind NAT firewalls and uses a distributed architecture with one or more supernodes to help discover network participants and route traffic.
NAT Firewall (Network Address Translation) – a service that translates addresses between a local area network (LAN) and the Internet. A computer on a private network typically receives a private IP address that is not directly reachable from the public Internet. NAT can prevent unsolicited inbound connections unless port forwarding or another rule is configured. It is not, by itself, a complete firewall or security solution.
NeoRouter VPNs – a networking application frequently used for remote access, peer-to-peer connections, and virtual private networks. NeoRouter can connect personal computers, servers, and other devices over the Internet to create a virtual network.
Network manager – a program that manages network connections and their settings. It can connect to specified wireless or wired networks and switch between available connections. Some network managers also support VPN connections through plugins.
‘Network-to-network’ connection – a site-to-site VPN connection that allows computers on one local network to access computers on another network. It is useful for linking networks in hybrid configurations and typically uses VPN gateways, often with IPsec. A ‘point-to-network’ connection allows an individual device to access a network remotely and typically uses VPN client software.
NSA (United States National Security Agency) – a US intelligence agency within the Department of Defense responsible for signals intelligence and protecting classified government information. Its work includes collecting and analyzing foreign communications intelligence.
Off-site user – a user who can access a computer or network remotely over the Internet using another device. The computer being accessed must be powered on and have remote access enabled. Depending on the setup, the user may need specific software or credentials.
Open Source Software – software whose source code is available under a license that permits users to inspect, use, modify, and redistribute it. This allows developers to review the code, adapt it, and contribute improvements.
OpenVPN – a VPN protocol and software implementation widely considered secure when configured appropriately. It creates an encrypted tunnel over an untrusted network, such as the Internet. OpenVPN supports a range of cryptographic algorithms and can be configured to use different ports and transport protocols, but setup may require additional software or configuration.
Overlay Network – a logical network built on top of another network. A VPN is one example: it operates over the Internet and adds a virtual network layer. Overlay networks can provide services that are not part of the underlying network, though they may add processing and routing overhead.
Password – a sequence of characters used as an authentication credential. It is intended to be known only to the user or authorized parties and helps prevent unauthorized access.
P2P (peer-to-peer network) – a distributed network in which participating nodes can perform similar functions and share resources. A peer can act as both a client and a server. Some P2P networks use dedicated servers for coordination, while others operate without them.
Phishing – a computer fraud technique based on social engineering. A phisher may create a copy of a legitimate resource, such as a bank website, and send messages that appear to come from the bank. The messages often ask users to confirm or change their details. The aim is to persuade users to follow a link and enter confidential information on a fraudulent site.
Password manager – software designed to manage and protect users’ passwords and PINs, usually by storing encrypted data in a local or cloud-based database. As an extra function, password managers may fill in username and password fields automatically, often through a browser extension. They can help reduce the risk of phishing when they only autofill credentials on the correct website.
Perfect Forward Secrecy (PFS) – a property of a secure communication protocol that helps ensure that the compromise of a long-term key does not expose past session keys. PFS is commonly provided through ephemeral key exchanges. Protocols such as IPsec, SSH, and TLS can support PFS when configured with suitable cipher suites.
Ping – a utility program used to test the reachability of a network host and measure round-trip time (RTT). It typically sends ICMP Echo Request messages and records incoming Echo Replies. Results can show latency and packet loss, but do not by themselves identify the cause of network congestion.
Point-to-point encryption (P2PE) – a method that encrypts data at the point where it is captured and protects it while it is transmitted over a network. In payment processing, for example, card data is encrypted at the point-of-sale device and remains encrypted until it reaches a secure decryption environment.
Port forwarding – a technology that redirects connection requests from an external network address and port to a selected machine and port on a local network. It is used when a service on a local computer needs to be reachable through a NAT router, for example, for some P2P applications or multiplayer games.
PPPoE (Point-to-Point Protocol over Ethernet) – a protocol for carrying PPP traffic over Ethernet networks. It is commonly used by Internet providers to authenticate users and manage connections. When PPPoE is enabled, a user may need to enter a username and password to connect to the provider. PPPoE itself does not provide encryption.
PPTP (Point-to-Point Tunneling Protocol) – a VPN protocol developed by Microsoft and other vendors for implementing VPNs over dial-up networks. It is built into many operating systems and is quick to configure, but its security is weak by modern standards and it is not recommended for protecting sensitive data.
Pretty Good Privacy (PGP) – a computer program and set of standards for encrypting and digitally signing email and files. PGP implementations use a combination of hashing, data compression, symmetric encryption, and public-key cryptography. OpenPGP is an open standard implemented by programs such as GnuPG.
Profile – a collection of data and settings used to customize an electronic environment. User profiles can be created in operating systems, computer programs, and websites. In Windows environments, profiles may be local, roaming, or mandatory. A mandatory profile is controlled by an administrator and is generally read-only for the user.
Protocol Types – a set of rules that enables computers to connect and exchange data over a network. Different protocols describe different aspects of communication and are often organized into suites. The OSI model classifies networking functions into seven layers:
- Physical layer transmits raw signals over a medium. Examples include Wi-Fi and Ethernet physical-layer standards.
- Data Link layer transfers frames between nodes on the same link and handles link-level addressing and error detection. Examples include Ethernet and PPP.
- Network layer handles logical addressing and routing between networks. Examples include IPv4, IPv6, and IPX.
- Transport layer supports end-to-end data transfer. TCP provides reliable, ordered delivery; UDP does not guarantee delivery or order.
- Session layer establishes, manages, and terminates communication sessions. Examples include RPC and NetBIOS.
- Presentation layer handles data representation, translation, compression, and encryption.
- Application layer provides network services to applications. Examples include HTTP, DNS, BitTorrent, and SMTP.
Proxy – a system that allows users to make indirect requests to other network services. When a client connects to a proxy server, it requests access to a web resource through the proxy. The proxy forwards the request and returns the response. Depending on its configuration, a proxy may mask the client’s IP address from the destination server or filter traffic.
Public key – a basic component of asymmetric cryptography. A public key can be shared over a network, unlike the corresponding private key, which must be kept confidential. Data encrypted with a recipient’s public key can be decrypted with the corresponding private key. For example, if Brad encrypts a message with Piet’s public key and sends it to him, Piet can decrypt it with his private key.
Remote Access VPN – a software or hardware-software system that allows users to connect securely to corporate network resources over public networks, usually the Internet. It uses security measures to protect the confidentiality and integrity of data transferred over untrusted channels. Some organizations use certified cryptographic gateways to meet legal or regulatory requirements.
Root certificate – a self-signed certificate belonging to a root Certificate Authority (CA) at the top of a chain of trust. Root certificates are distributed through trusted certificate stores and are used to validate certificates issued by subordinate authorities. Certificates contain a public key and related information, such as the subject, validity period, and permitted uses.
Router – a network device or software that forwards data packets between networks. It can connect networks with different architectures. Using routing tables and configured rules, a router selects where to send packets based on their destination addresses. If it has no suitable route, it may drop the packet or send it to a default route.
RSA encryption – a public-key cryptographic method using the RSA algorithm, in which the public key and private key are different. The public key can be shared, while the private key is kept secret. RSA can be used for encryption and digital signatures, though modern systems commonly use it to establish or protect symmetric keys rather than to encrypt large amounts of data directly.
RSA Security – a US-based computer and network security company known for developing and commercializing RSA-related security products, including SecurID authentication technology.
Safe Harbor Framework – a system based on an agreement between the United States and the European Union that allowed participating US organizations to transfer personal data from the EU while following specified privacy principles. It was invalidated by the Court of Justice of the European Union in 2015 and later replaced by other frameworks.
Secret key – a key used to encrypt and decrypt data in symmetric cryptography. It must be kept confidential by authorized parties. If an unauthorized person obtains the key, they may be able to decrypt data protected with it.
Shared IP address – an IP address assigned to multiple users or accounts on a server, rather than a unique address for each one. Shared addresses can reduce costs for VPN providers and may make it harder to associate traffic with an individual user. They do not guarantee anonymity.
Server – a computer or software system that provides services to other systems. A web server receives HTTP requests from browsers and returns responses, which may include HTML pages, images, files, or other content. A VPN server accepts VPN connections and helps provide access to a network or route traffic.
Simultaneous connections – the ability to use one VPN service on multiple devices at the same time. These may include routers, computers, or mobile devices. The number and types of devices allowed depend on the VPN provider and subscription.
SmartDNS – a service that reroutes selected DNS requests to help users access region-restricted content or blocked websites. Unlike a VPN, SmartDNS generally does not encrypt all traffic or hide the user’s IP address.
SMTP (Simple Mail Transfer Protocol) – a widely used network protocol for sending email over TCP/IP networks. SMTP is used to submit and relay outgoing messages, commonly over ports 25, 465, or 587. Email clients generally use POP or IMAP to retrieve messages.
Software audit – an examination of an operating system, software product, or development process by one or more auditors who are independent of its development. The audit assesses compliance with requirements, standards, instructions, plans, or procedures and provides an independent evaluation.
Source Available – software whose source code can be inspected, but whose license does not necessarily permit modification or redistribution. Some source-available licenses are not considered open-source licenses under the Open Source Definition.
Split tunneling – a configuration that allows a device to access public networks through the same physical connection used for a VPN. Traffic selected for the VPN passes through the encrypted tunnel, while other traffic is routed through the local network interface. Split tunneling can reduce VPN bandwidth use, but traffic routed outside the tunnel is not protected by the VPN.
SSH Tunneling – the forwarding of TCP traffic through an encrypted SSH connection. Depending on the configuration, traffic may be forwarded between local and remote ports or through an intermediate host. SSH tunneling generally supports TCP forwarding, not arbitrary traffic without additional mechanisms.
SSH2 – the second version of the SSH (Secure Shell) protocol. It provides an encrypted channel for exchanging data over a network and can be used to transfer files or run programs securely. SSH-2 replaced the less secure SSH-1 protocol.
SSL/TLS (Secure Socket Layer/Transport Layer Security) – cryptographic protocols that provide communication security over a computer network. SSL is an older protocol; TLS was developed as its successor. SSL is deprecated, while current systems use TLS to protect information transmitted by websites, email, and other applications.
SSL/TLS certificates – digital certificates used to authenticate a server or other entity during a TLS connection. They bind a public key to an identity, such as a domain name, and are usually issued by a Certificate Authority. Certificates are used during the TLS handshake to help authenticate the server and establish a secure connection.
SSTP (Secure Socket Tunneling Protocol) – a Microsoft VPN protocol that carries PPP traffic over a TLS connection, commonly using TCP port 443. It is available in supported versions of Windows and some other systems. SSTP uses TLS for the secure channel and PPP-based methods for user authentication.
Static VPN IP – a fixed IP address assigned to a user’s VPN connection. It generally remains the same between sessions, although the provider may change it. A user may also be able to change it manually, depending on the service.
Strong cryptography – cryptographic algorithms and implementations that resist known cryptanalysis and require impractical computational resources to break when used with appropriate keys. No cryptographic system should be assumed to be completely unbreakable.
STUN server – a server that allows NAT clients to discover their public IP address and the port mapping assigned by the NAT device. This information can help establish UDP connections with VoIP providers and other peers. STUN is defined in RFC 5389; RFC 3489 was an earlier specification.
Supercookies – a class of tracking mechanisms that store or recreate persistent identifiers outside standard browser-cookie storage. They can be harder to detect and remove than regular cookies. Their methods vary and may include alternative browser storage or identifiers added to network traffic.
TCP (Transmission Control Protocol) – a core transport-layer protocol in the TCP/IP suite. TCP establishes a connection and uses sequence numbers, acknowledgments, and retransmissions to provide reliable, ordered delivery of data. It also manages flow and congestion control.
TCP/IPv6 – the use of the TCP/IP protocol suite with IPv6 addressing. IPv6 is supported by many modern operating systems and Internet providers, though availability and configuration vary by network.
Targeted ads – online advertisements selected for particular audiences or users based on factors such as browsing activity, interests, location, or demographic information. Targeting may use cookies and other tracking technologies.
The Golden Shield Project – a Chinese government project for monitoring and controlling network access and information. It is associated with the Great Firewall of China, which uses measures such as IP blocking, DNS filtering, and URL keyword filtering. Services such as Baidu, Sina Weibo, and Youku Tudou are examples of domestic alternatives to some foreign platforms.
Threat model – a documented analysis of potential security threats to a system, including the conditions and factors that could lead to unauthorized access, data destruction, modification, or disclosure. A threat model helps define security requirements and select appropriate safeguards.
Tor hidden services – services with `.onion` addresses that are accessible through the Tor network. Connections are established through Tor rendezvous points, allowing both the service and its users to conceal their network locations. The service can be hosted behind NAT or a firewall.
Tor (The Onion Router) – a system that routes traffic through a network of relays to help protect users against some forms of surveillance and traffic analysis. Tor users can browse the web with increased privacy using the Tor Browser. Traffic is encrypted in layers and each relay removes one layer, but Tor does not guarantee complete anonymity or encrypt traffic beyond the exit relay unless the destination connection is otherwise secured.
Trojan horse – a malicious computer program disguised as legitimate software. It may collect and transmit information, damage or alter data, or disrupt system operation. To reduce the risk of infection, users should avoid downloading files from suspicious sources, keep security software up to date, and scan unfamiliar files before opening them.
Two-factor authentication – a user verification method that requires authentication data from two different factors, providing an additional layer of account protection. For example, a user may enter a password and then approve a prompt in an authenticator app or use a security key. Two-factor authentication reduces risk but does not guarantee protection from account compromise.
UDP (User Datagram Protocol) (User Datagram Protocol) – one of the core protocols in the TCP/IP suite. It allows hosts to exchange datagrams over an IP network without establishing a connection. UDP does not guarantee delivery, ordering, or error recovery, so packets may be lost without the sender or receiver being notified.
URL (Uniform Resource Locator) – an address that identifies a resource and indicates how to access it. A URL may include a scheme, domain name, and path to a webpage or file.
USA Freedom Act – a US law enacted in 2015 that changed certain surveillance authorities, including ending the NSA’s bulk collection of domestic telephone metadata under Section 215 and requiring targeted orders for access to such records.
USA Patriot Act – a US federal statute enacted in 2001 that expanded law enforcement and intelligence agencies’ surveillance and investigative powers, including certain wiretapping and information-gathering authorities.
VLAN (Virtual Local Area Network) – a logical network operating at Layer 2 of the OSI model. It groups end stations even when they are connected to different physical network segments. VLANs can simplify network management, divide broadcast domains, and help isolate traffic.
VPN (Virtual Private Network) – a technology designed to transmit data through a protected tunnel over an untrusted network. A VPN can encrypt traffic between a client and a VPN server and may change the IP address visible to websites. It can help protect traffic on public Wi-Fi and provide access to remote networks or region-restricted content, but it does not guarantee anonymity or prevent all threats.
VPN client – software downloaded from a VPN provider’s official website and installed on a personal device to connect it to the VPN service. Software designed for mobile platforms is usually called a VPN app. VPN clients support different protocols, such as OpenVPN, IKEv2, and WireGuard; features vary by provider.
VPN connection – a connection established through a VPN tunnel. A VPN may affect Internet speed because traffic is routed through a VPN server and encrypted. Server distance and load, the user’s ISP and plan, and the capabilities of the user’s computer or mobile device can also affect speed.
VPN security gateway – a network device connected to multiple networks that can encrypt and authenticate traffic for hosts behind it. Traffic intended for internal corporate networks passes through the gateway, where security rules can be applied. It may be implemented as software, a hardware device, or a router with VPN functions.
VPN software – software, procedures, and configuration files used to create and manage VPN connections. VPN software can connect devices or networks and may provide access to remote network resources. Examples include OpenVPN software and built-in VPN clients in operating systems.
VPN service – a service that provides VPN connections through its servers. VPNs can help protect traffic on public Wi-Fi and route it through a remote server. Features such as peer-to-peer file sharing, server locations, encryption, and connection limits vary by provider.
VPN tunnel – an encrypted, encapsulated communication channel between a device and a VPN server, or between two network endpoints. It carries data across an underlying network, such as the Internet.
Warrant canary – a published notice stating that a company has not received certain government orders up to a specified date. If the notice is removed or no longer updated, readers may infer that the company has received such an order. A warrant canary’s legal effect and reliability may vary.
Web accelerator – software designed to reduce webpage loading times by caching resources, compressing data, or pre-fetching pages a user is likely to open. Google released a Web Accelerator product in 2005, but it was discontinued.
WebRTC – an open-source project that enables real-time communication, including voice, video, and data transfer, between browsers and other supported applications. It can support peer-to-peer connections and is also used by servers and services.
Wi-Fi hotspot – an area where people can access a network wirelessly using a device with a Wi-Fi adapter. Offices, underground stations, hotels, libraries, and shops may provide Wi-Fi hotspots.
Zombie cookies – cookies or tracking data that are recreated after deletion, typically using copies stored in other browser storage locations. They can be used to restore identifiers for tracking, although the specific methods and providers vary.
Comments